Who changed what, and from where?
Oracle and SQL Server activity on record with a risk score; ports, CVEs and password policy scanned on a schedule.
The problems it solves
Nobody records who changed what in the database.
Activity monitoring →Exposed ports and known CVEs slip through.
Security checks →Weak password policies go unnoticed.
Security checks →The features that do it
Activity monitoring: who changed what, from where?
The Audit Investigation Center scores Oracle and MSSQL activity by risk in one audit trail: bulk deletes, after-hours activity, shared service accounts and failed statements surface instantly. On Oracle the source is Unified Auditing; on MSSQL the traffic is captured off the network — no Extended Events, no trace.
- Automatic risk score on every record (bulk, after-hours, shared-account signals)
- User / object / program breakdowns, full-text SQL search and activity timeline
- On SQL Server, passwords and tokens are masked on the host; SQL text can be dropped
- CSV and JSON exports, signed PDF report (Oracle), dedicated auditor role
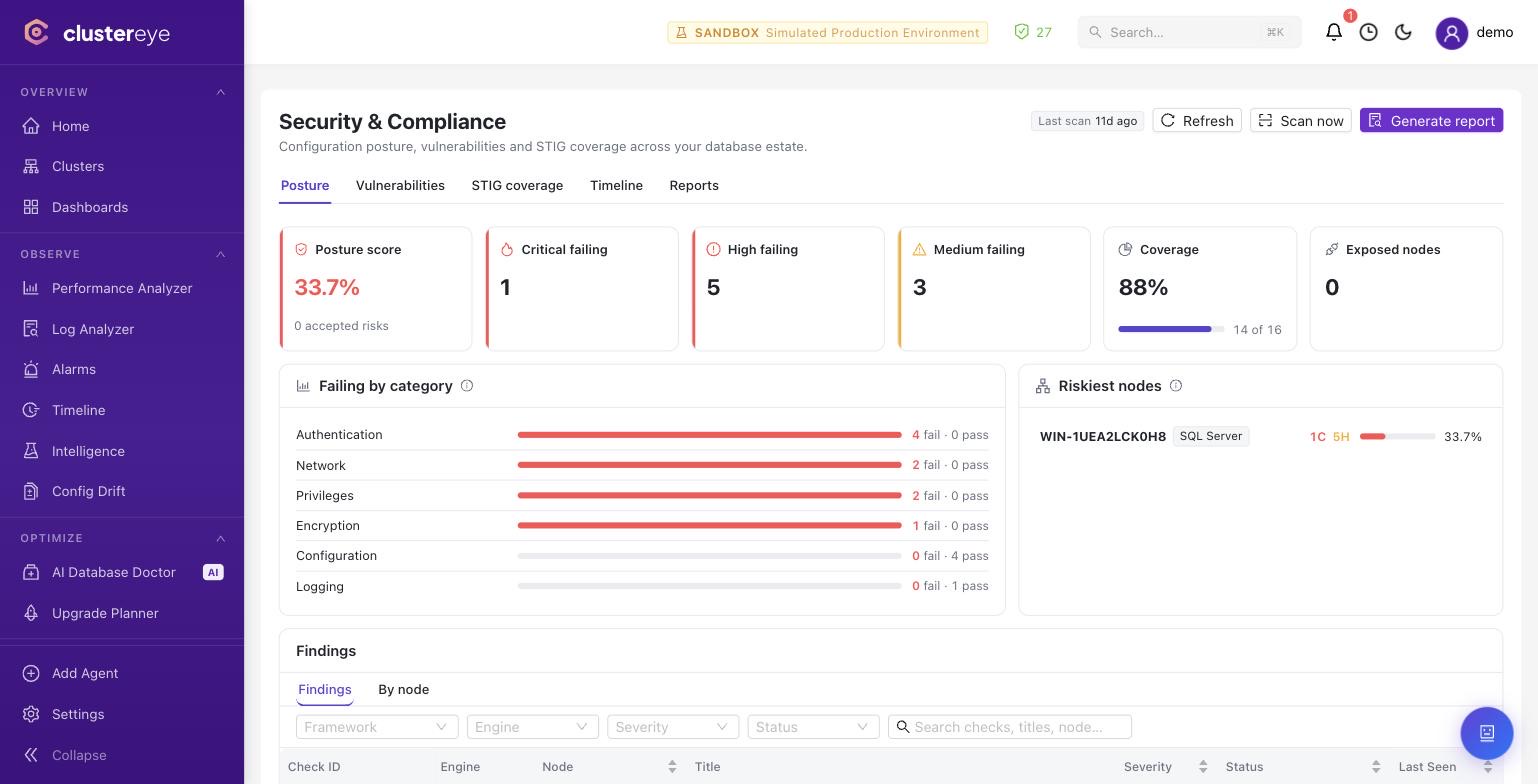
Security audit for compliance
Scan on a schedule for exposed ports, public access, known CVEs and weak password policies. Findings map to CIS and NIST 800-53, with crosswalked scorecards for ISO 27001, PCI-DSS, SOC 2 and GDPR.
- CVE matching with fixed-version patch status
- RBAC, LDAP login, tamper-evident user audit log
- Compliance scorecards through the NIST 800-53 crosswalk
See it in your team's environment.
A demo with your engines and your questions.